See every door your infrastructure leaves open.
Périmètre finds everything your organisation exposes on the Internet, including what nobody remembers, shows you where an attacker would strike first, and tells you how to fix it.
From one domain to everything you expose, and how to secure it.
Map it from a domain
Start from what you know: your domains. Périmètre shows what you really have online, shadow IT included: the forgotten test server, the agency’s microsite.
Findings you can act on
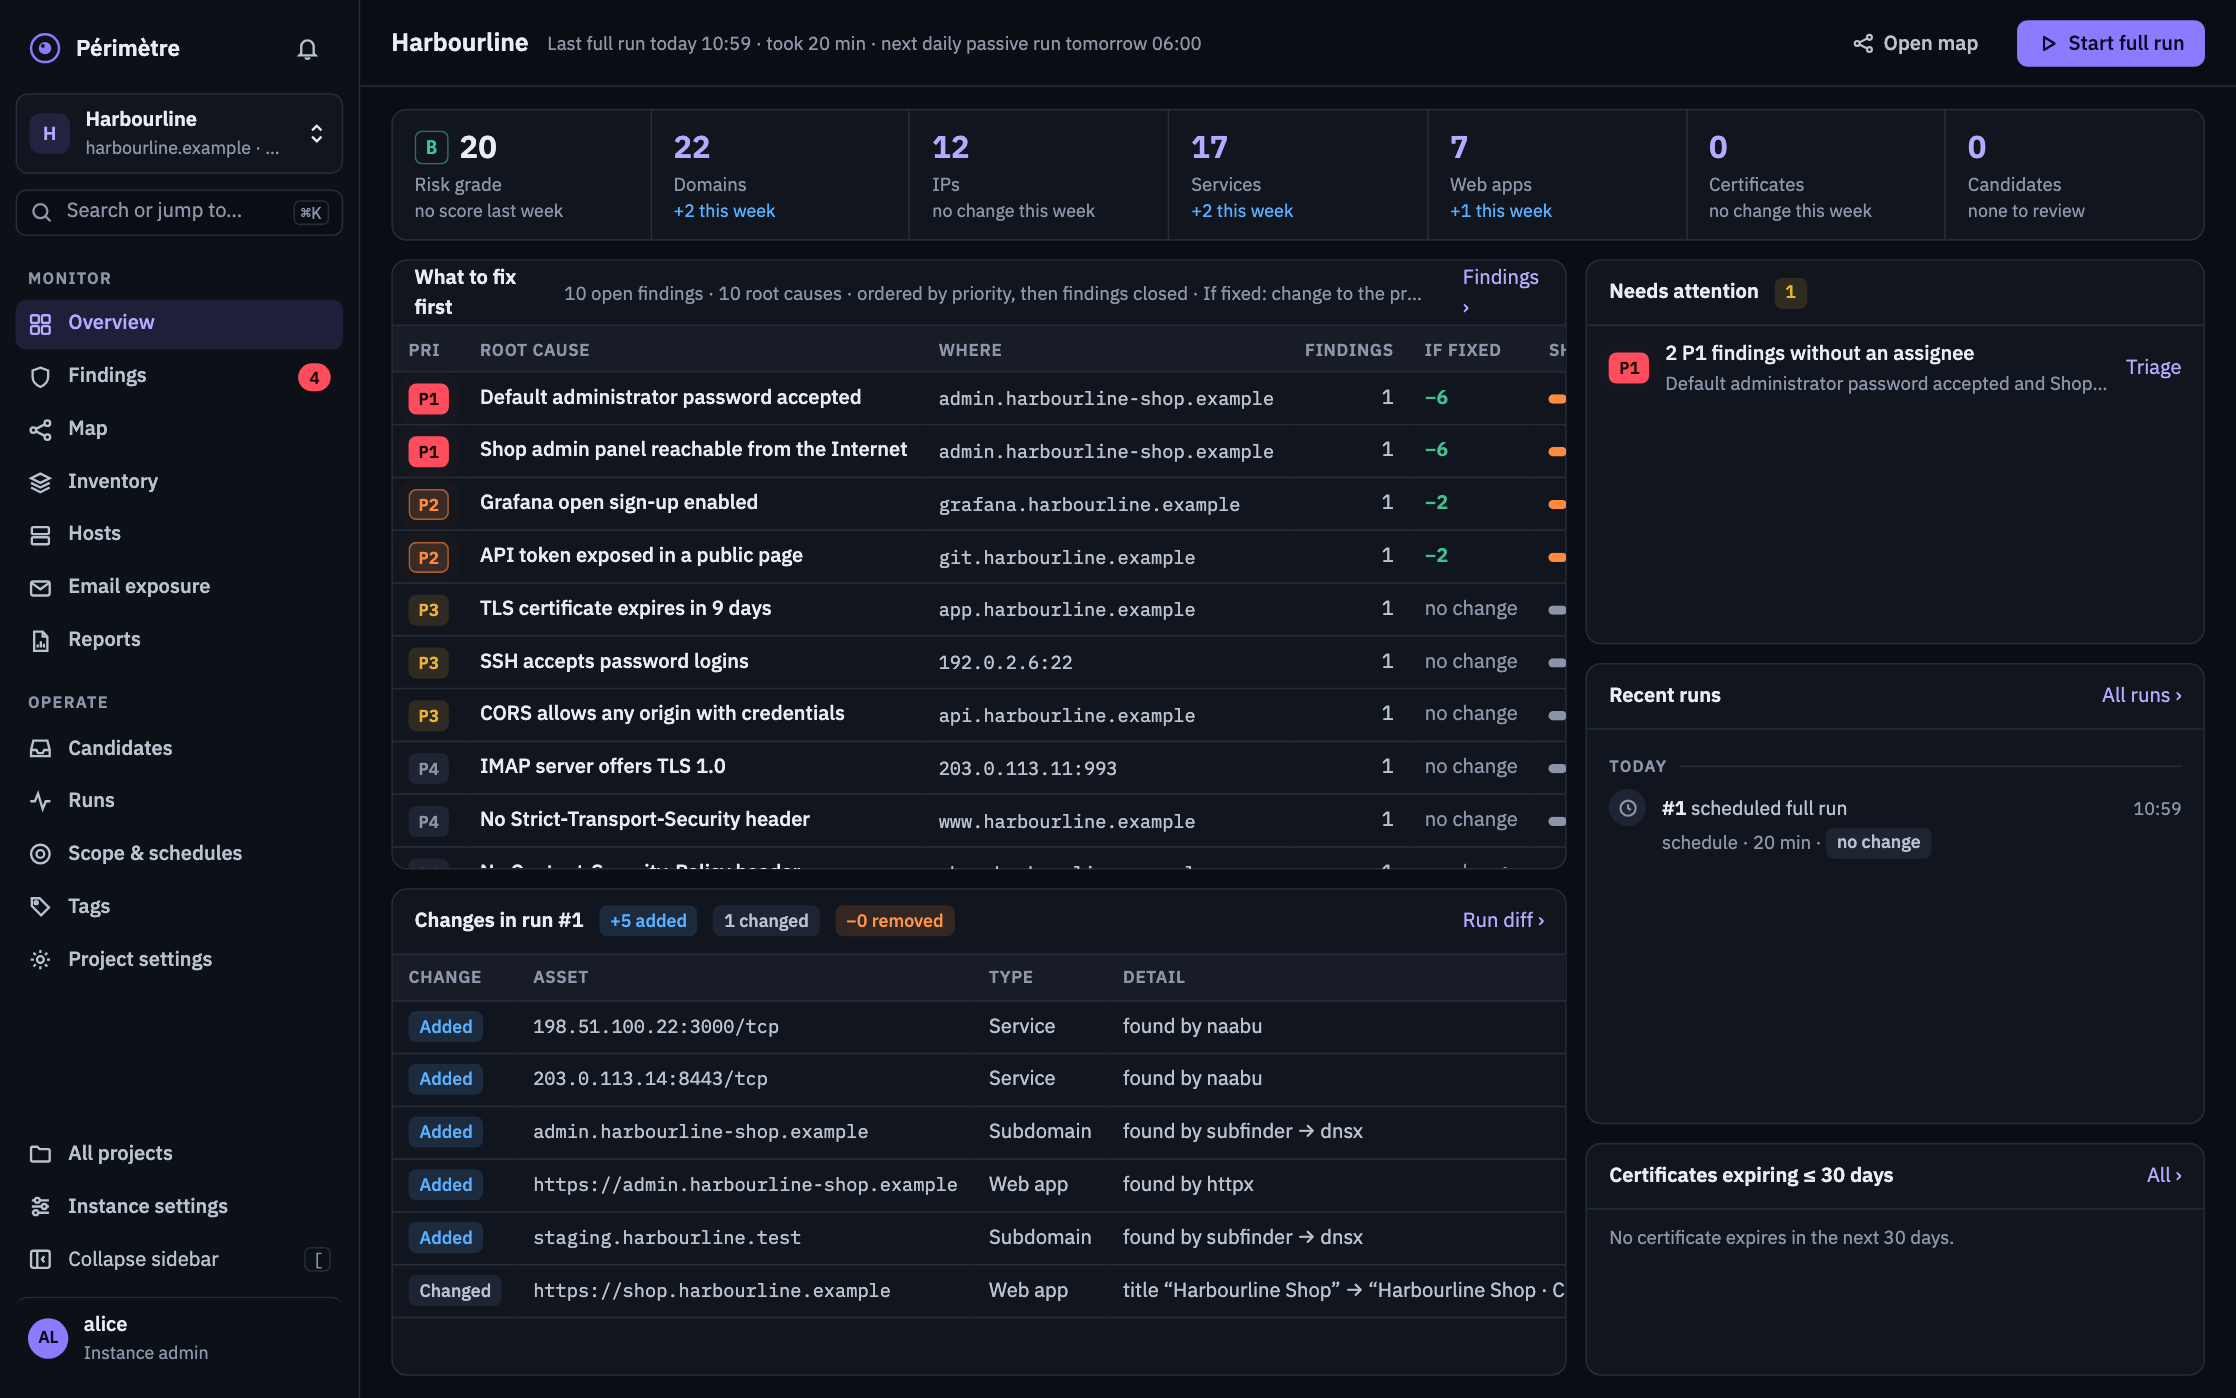
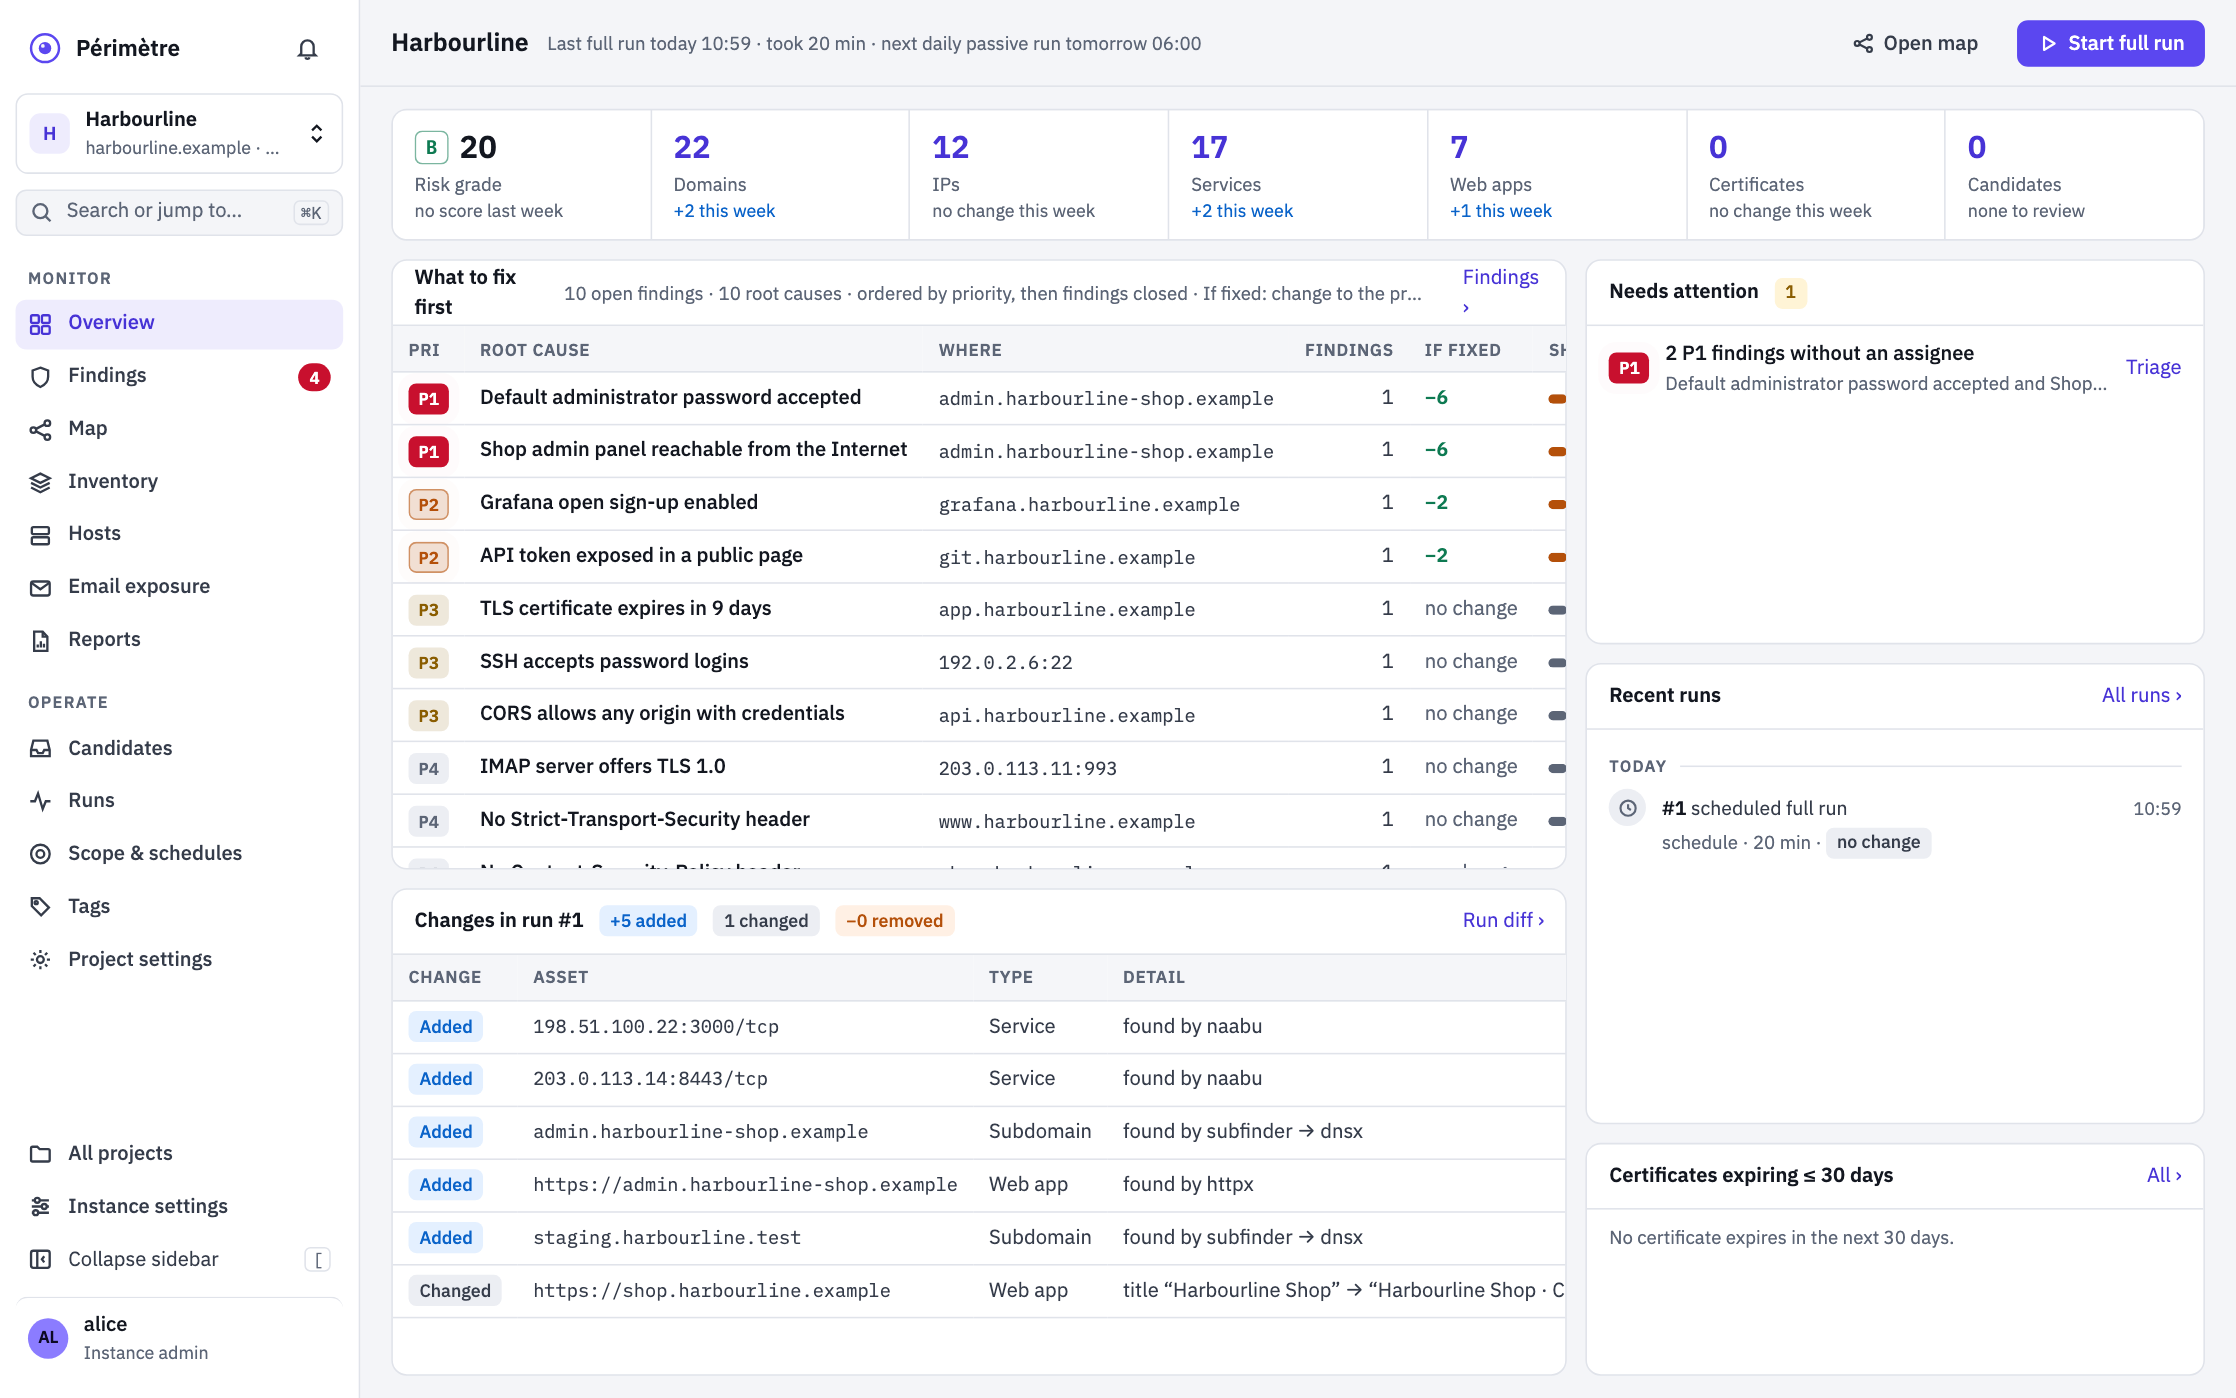
Not just a diagnosis: each finding says what is at risk and how to fix it, worst first. Périmètre checks again once it is fixed, and when a new CVE lands.
Alerts and reports
Email, Teams and Telegram alerts for what matters, and clear weekly or monthly reports for management.
Ask your AI assistant
Connect Claude or another assistant: it reads your map and findings, explains them and helps you prioritise.
Protect your Microsoft 365
Microsoft 365 is an attack surface too, and the one most teams forget. Connect your tenant read-only: Périmètre checks MFA, admins, guests, apps and mail forwarding against the CISA and CIS baselines.
An optional host agent
Périmètre works from the outside, with nothing to install. Add the read-only agent where you choose to see what no outside scan can: real listeners, vulnerable packages, the firewall.
A risk score you can explain, on every asset.
Every asset gets a score from 0 to 100 and a grade from A to F, so you know at a glance where to start. Every point comes from a finding you can open, with fixed, documented weights: no black box, and a clear answer when your management asks how exposed you are.
- Known exploited, likely exploited (EPSS) and overdue findings weigh more
- A reachable login page and a name listed in certificate logs add points
- Tag your important assets: they count ×1.5
- See how far fixing one root cause lowers the score
Risk score
How it’s computed ›Made for the daily work of a security team.
The whole team works from the same picture: what changed since the last scan, what to fix first and who is on it. No more spreadsheets, no more findings lost in an inbox.
Simple prices. Every feature in every plan.
You pay only for assets: the public hostnames and IP addresses in your scope. Ports, web apps, certificates, candidates, third parties and host agents are not counted. Users are unlimited on every plan.
Starter
€149 / month
or €1,490 a year, 2 months free
- Up to 50 assets
- 1 project
- Unlimited users
Team
€449 / month
or €4,490 a year, 2 months free
- Up to 200 assets
- 5 projects
- Unlimited users
Business
€1,190 / month
or €11,900 a year, 2 months free
- Up to 600 assets
- Unlimited projects
- Unlimited users
Enterprise and on-premise
More than 600 assets, or Périmètre installed on your own servers. On quote.
Every plan includes
- The isometric map and the asset inventory
- Vulnerability checks, retests on new CVEs and the risk score
- The read-only Microsoft 365 connector
- Email, Teams and Telegram alerts, scheduled reports
- The read-only host agent
- The MCP server for AI assistants
Waitlist offer: 30% off your first year for everyone who joins before launch.
More assets: €100 a month for each extra 50. Prices in euros, excluding VAT.
Want early access?
Write to us and we’ll tell you when Périmètre opens to new teams.
or write to waitlist@perimetre.app